8:00 - 5:00
Mon - Fri
AI
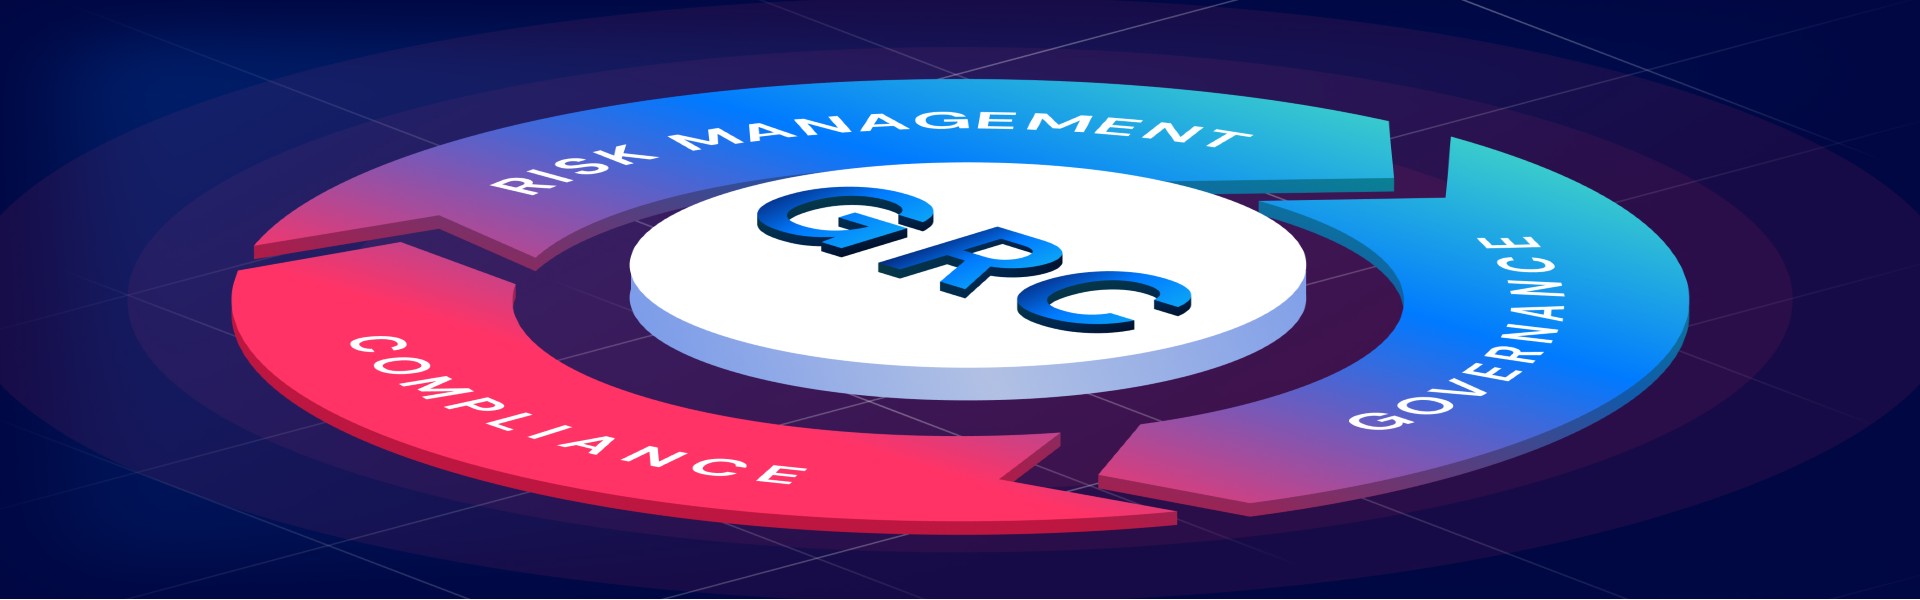
Governance, Risk, and Compliance (GRC) refers to an integrated approach that aligns business strategies with IT while ensuring risk management and regulatory compliance. By utilizing GRC tools and frameworks, organizations can streamline governance and risk processes while adopting new technologies efficiently. GRC helps organizations achieve theirobjectives, manage uncertainty, and meet regulatory requirements.
GRC is based on collaboration across various departments, ensuring that governance, risk management, and compliance work together seamlessly. Key stakeholders involved in the GRC process include:
GRC stands for Governance, Risk Management, and Compliance. In the past, businesses often addressed these areas separately. However, GRC combines them into one cohesive framework. By uniting governance, risk management, and compliance, businesses can improve efficiency, reduce errors, and enhance communication and information sharing across teams.
| Governance | Risk Management | Compliance |
| Governance refers to the policies, rules, and frameworks that guide a company toward its objectives. It defines responsibilities for key roles, like the board of directors and senior management, and ensures that all actions align with business goals. Effective governance promotes accountability, ethical decisionmaking, transparency, and proper resource management. | Risk management helps organizations identify and address potential risks— whether financial, legal, strategic, or security-related. A well-structured risk management program allows businesses to predict problems and reduce losses. For example, companies may assess security risks in their systems and implement measures to close any gaps. | Compliance involves adhering to relevant laws, regulations, and industry standards, as well as internal policies. In GRC, compliance ensures that business activities are conducted in accordance with legal and regulatory requirements. For instance, healthcare organizations must comply with privacy laws like HIPAA to protect patient data |